4 min read
Building this Blog How I rebuild my instances to use gp3 EBS volumes
How I rebuild my instances to use gp3 EBS volumes
Alwasy remember to set alerts for expiring reserved instances
Secure AWS by using short lived credentials...
Trigger AWS CodeDeploy from S3 event via Lambda...
Sharing S3 buckets across different AWS accounts is a very common practice and with encryption being more important now than ever, especially in certain industries like finance where security mandates us to enable SSE (Server Side Encryption) on all our buckets.
Have you ever need to refactor your Terraform code?
In AWS there is a limit on the amount of rules we can have in security groups. The current limit is 60 inbound and 60 outbound rules per security group. We can also attach up to 15 security groups per ENI (Elastic Network Interface). So 60\*15 will give us up to 900 inbound rules but we cannot exceed over 1000 rules for both inbound and outbound rules combined.
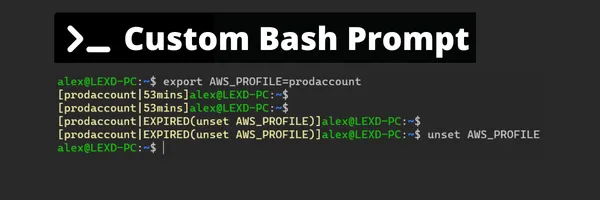
A custom bash prompt to show AWS credential expiration
Send email notification when jumpbox uptime exceeds the defined threshold...
Script to auto start/stop jumpbox on AWS to save cost...
Any time you attach an EBS volume to an instance, it will trigger a Lambda function which will then tag the volume by using the attached instance tags.
In GitHub Actions, create a container action to upload to S3...
Replacing MicroK8s with K8s created by kubeadm on EC2 instances...
Tags on AWS is very useful. It can be used for billing, identifying resources and filtering etc...
When you have dozens of AWS accounts to manage, e.g. dev, test, staging, prod etc. then IAM roles can also be used to allow for cross account access. This way you do not need to create multiple IAM users in each of those accounts.
AWS security groups is the foundation on how network access is granted to any EC2 resources. The definition which AWS uses is that...